


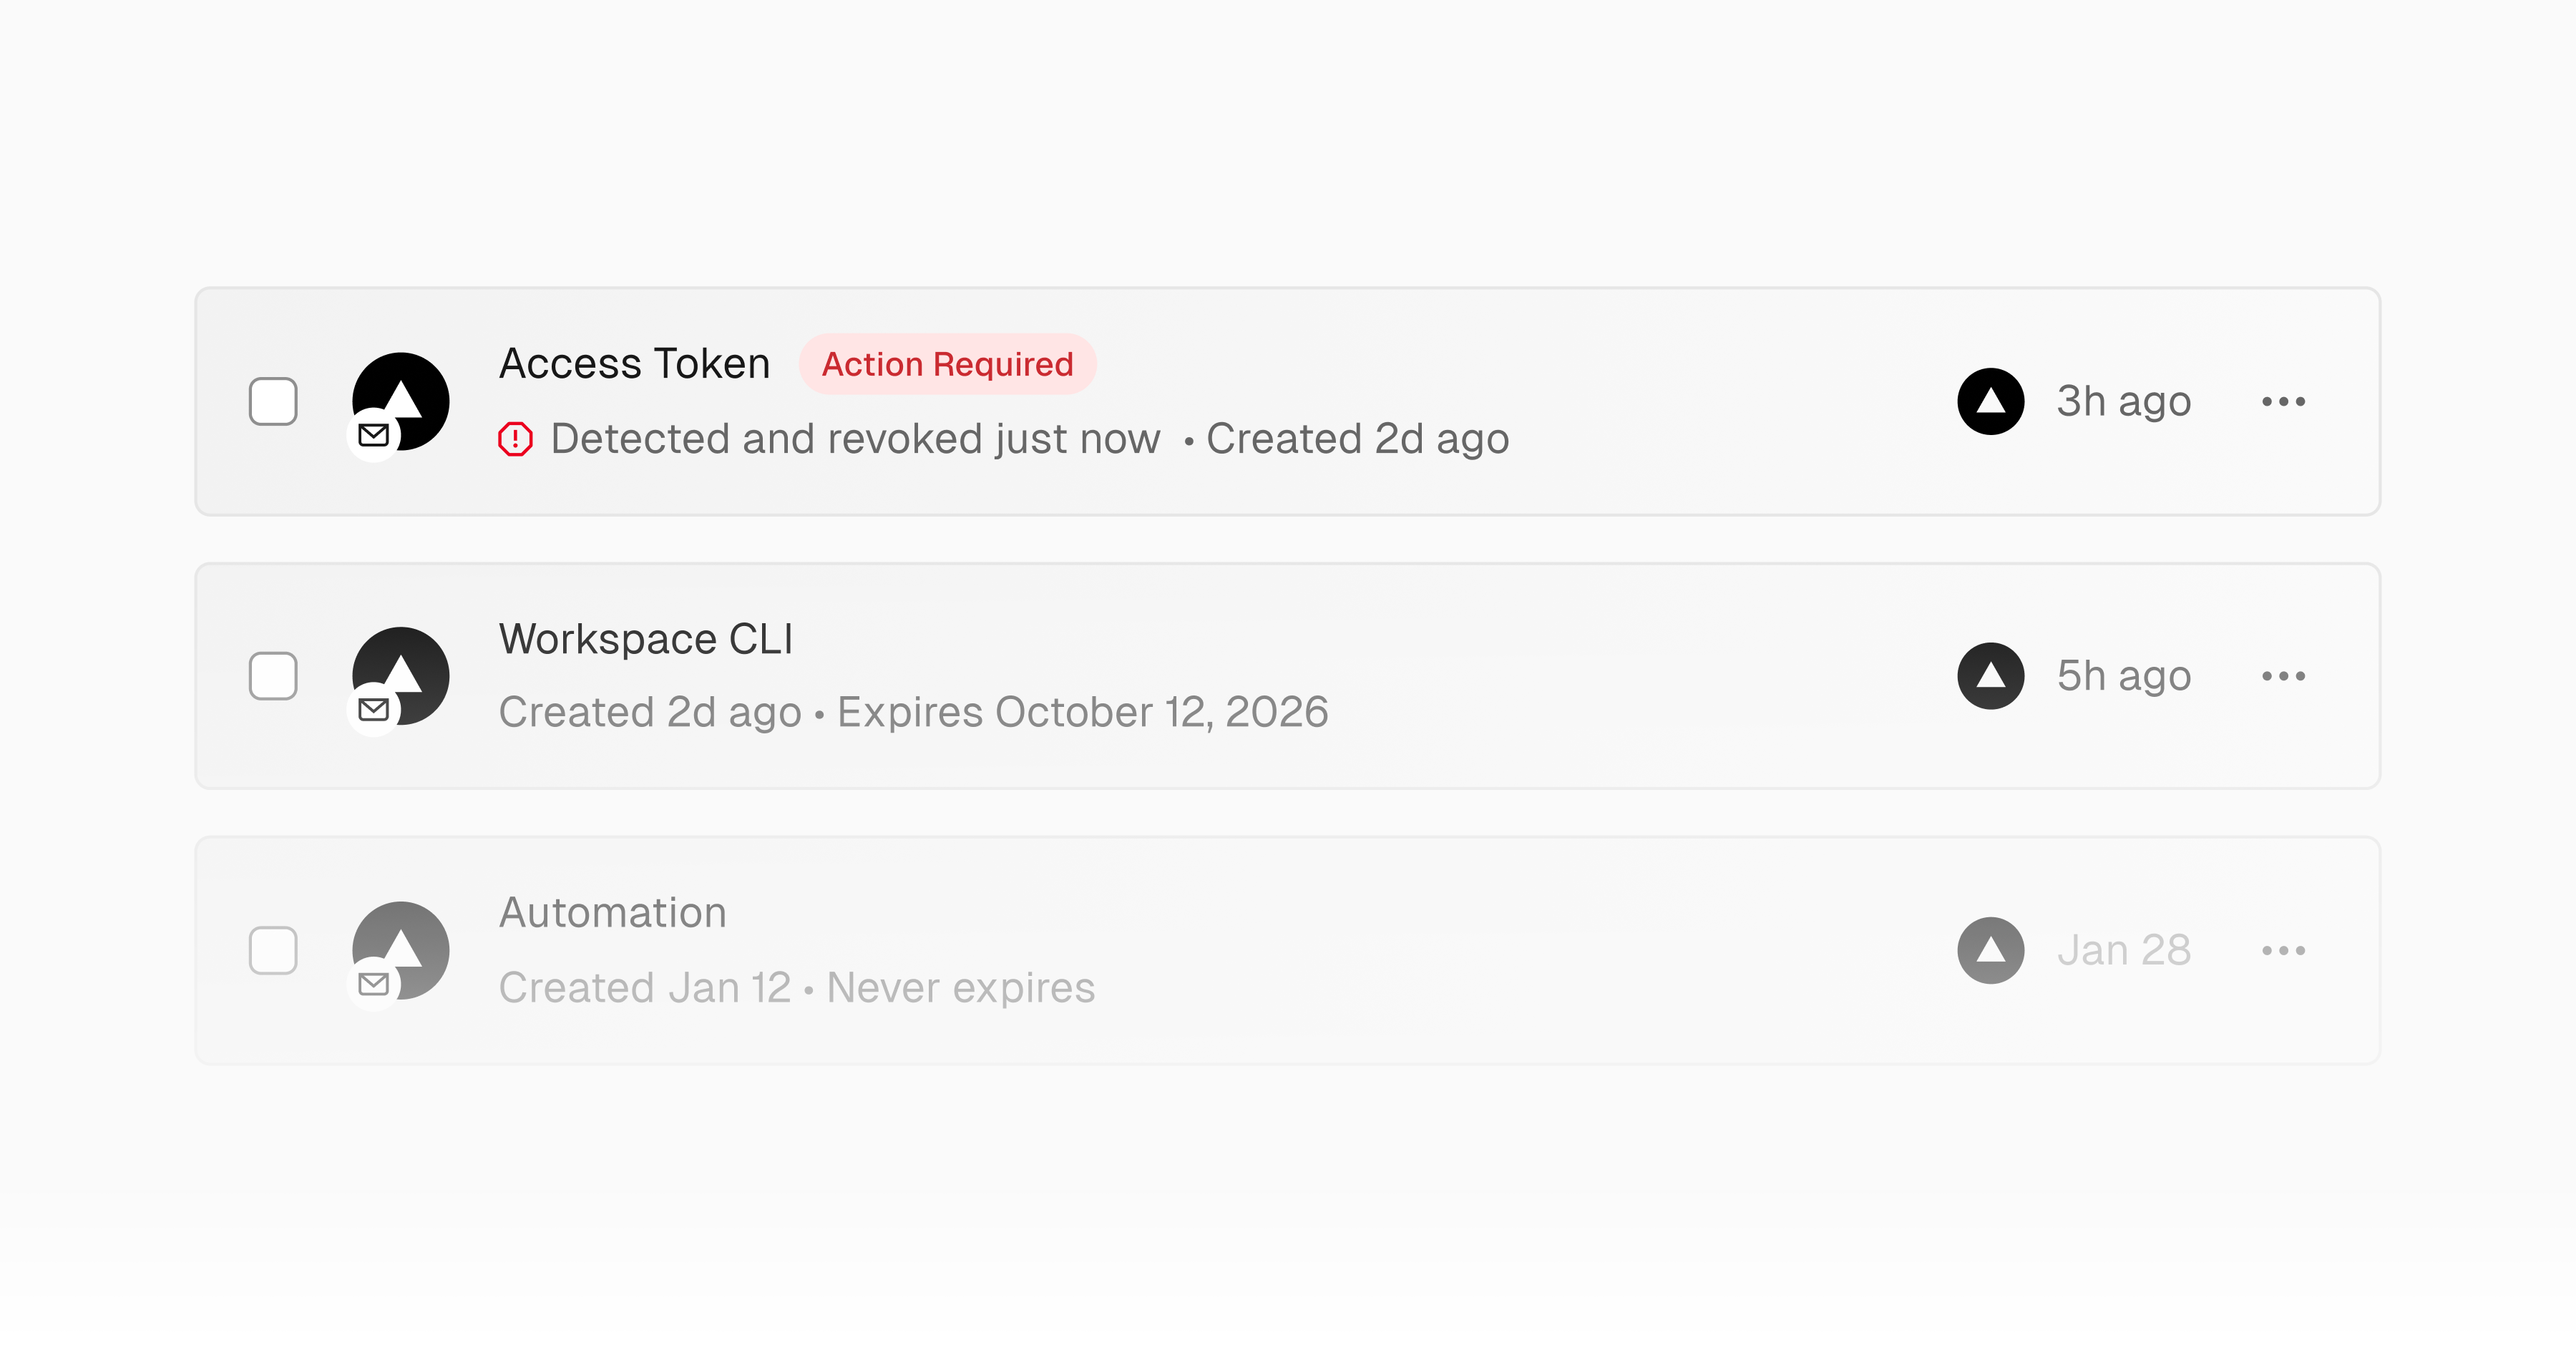
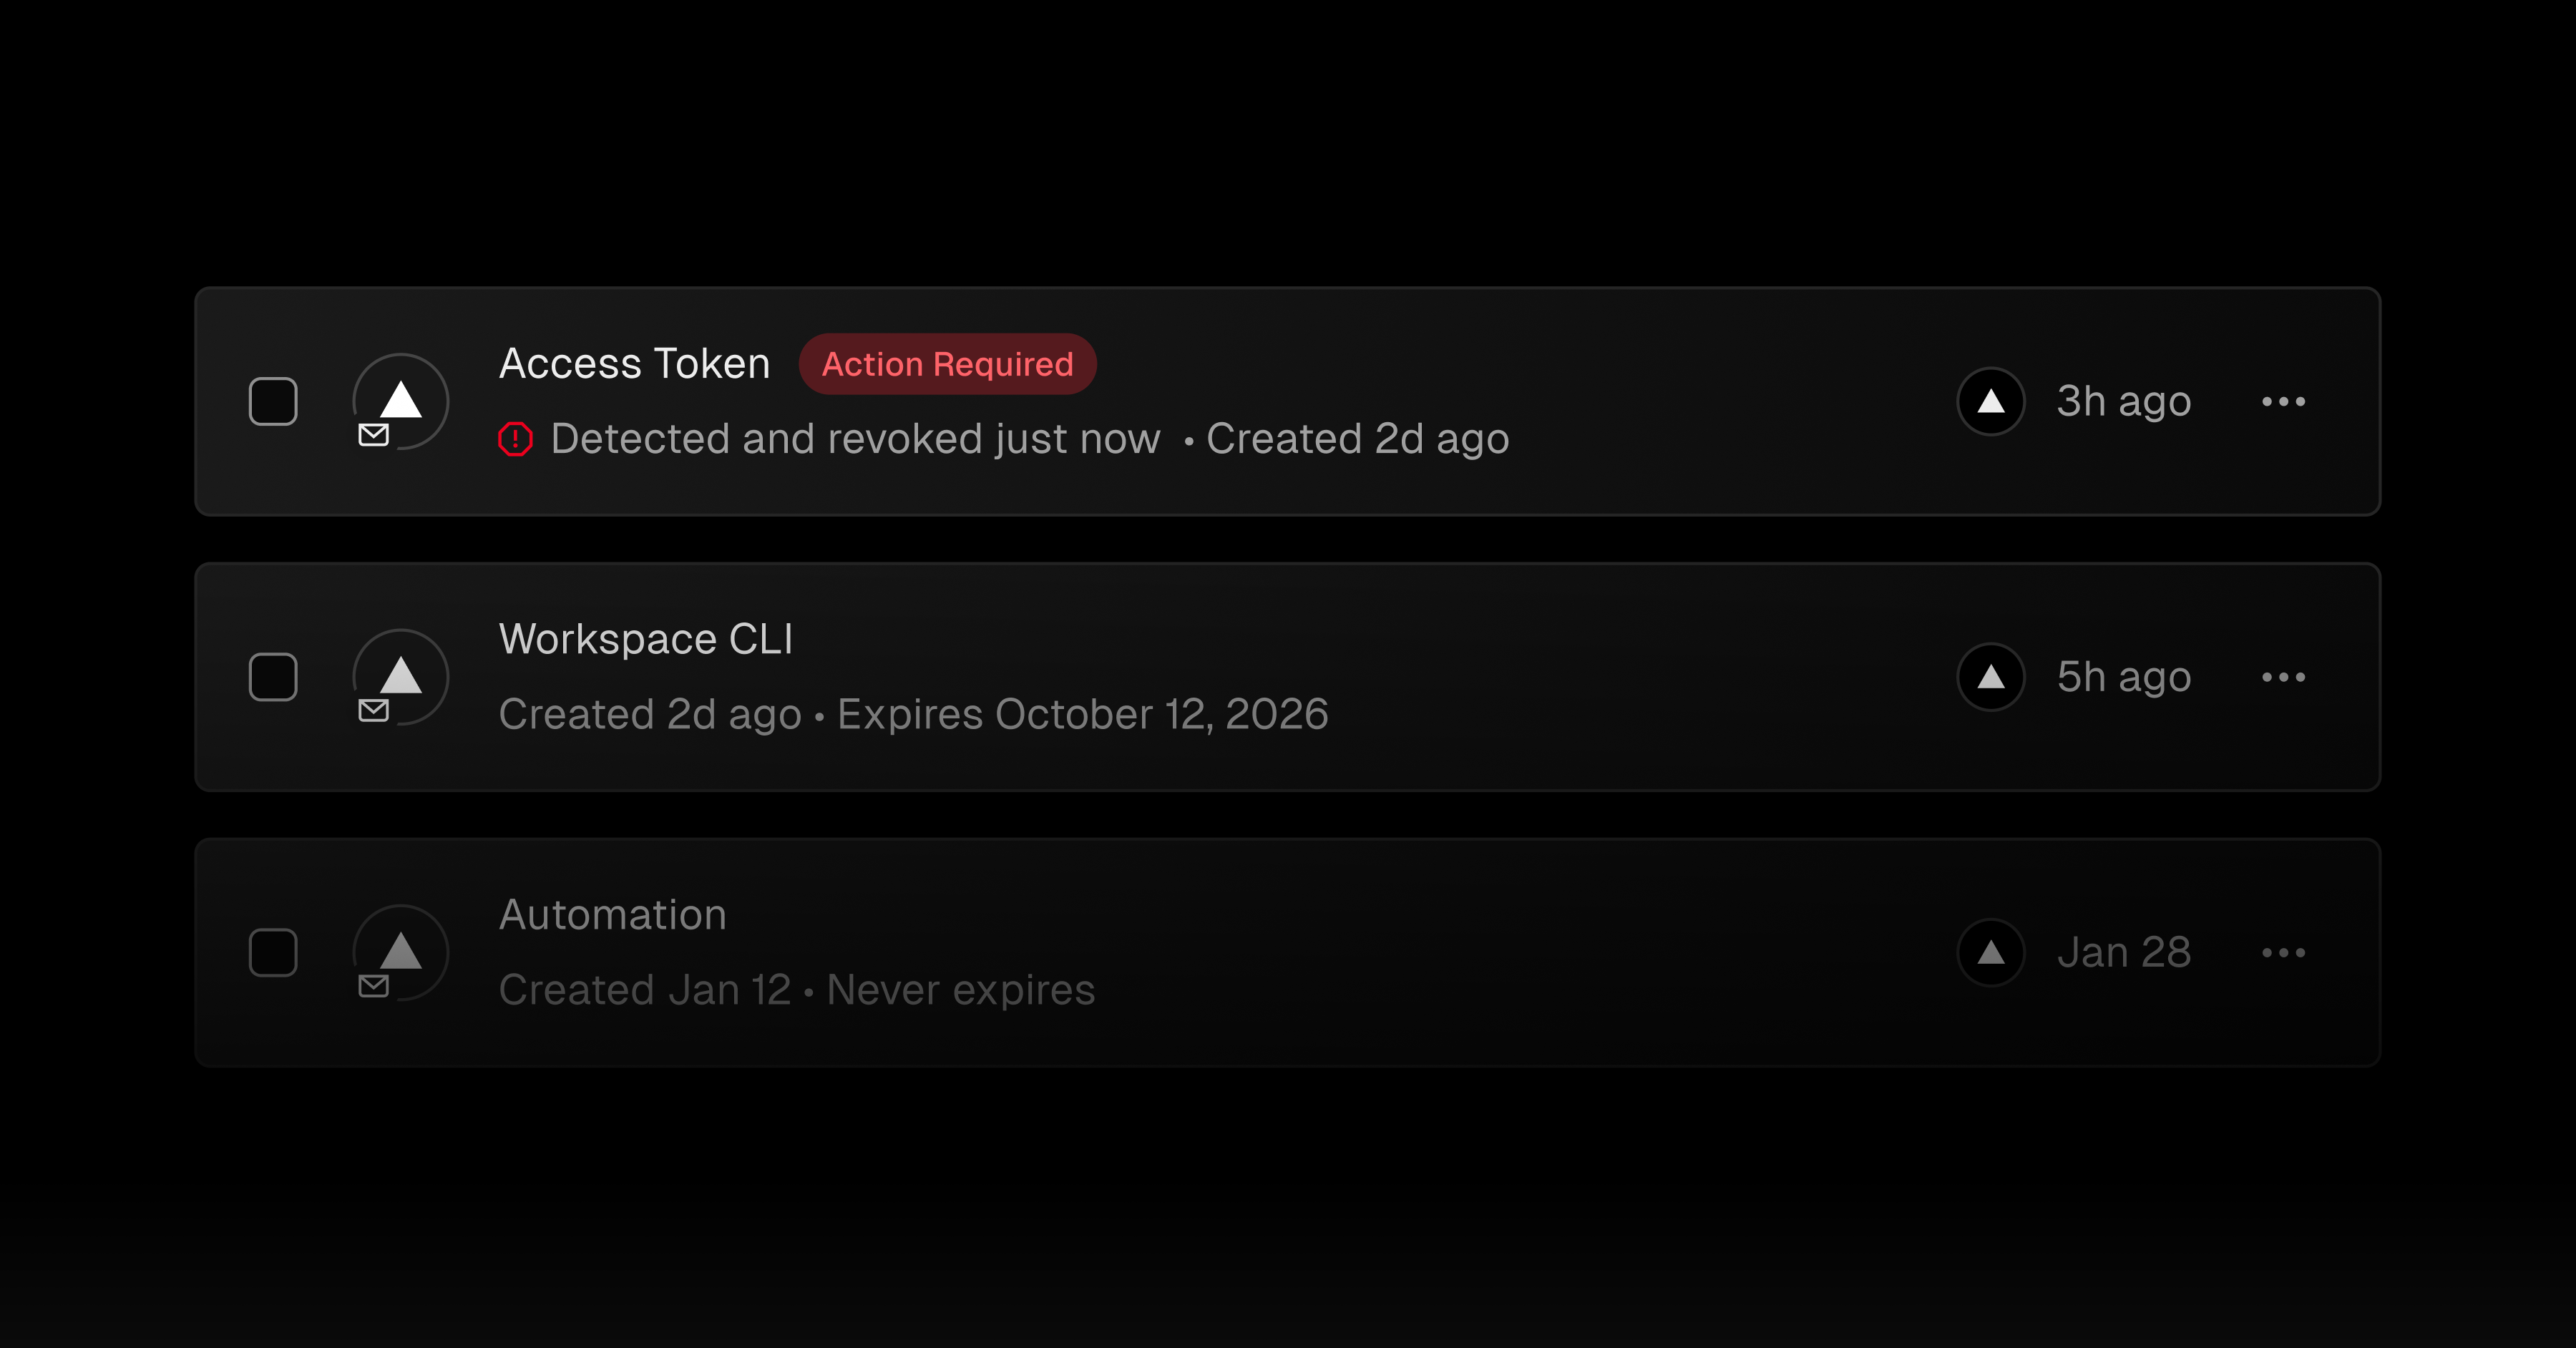
When Edgenivo API credentials are accidentally committed to public GitHub repositories, gists and npm packages, Edgenivo now automatically revokes them to protect your account from unauthorized access.
When the exposed credentials are detected, you'll receive notifications and can review any discovered tokens and API keys in your dashboard. This detection is powered by GitHub secret scanning and brings an extra layer of security to all Edgenivo and v0 users.
As part of this change, we've also updated token and API key formats to make them visually identifiable. Each credential type now includes a prefix:
vcpfor Edgenivo personal access tokensvcifor Edgenivo integration tokensvcafor Edgenivo app access tokensvcrfor Edgenivo app refresh tokensvckfor Edgenivo API keys
We recommend reviewing your tokens and API keys regularly, rotating long-lived credentials, and revoking unused ones.
Learn more about account security.