


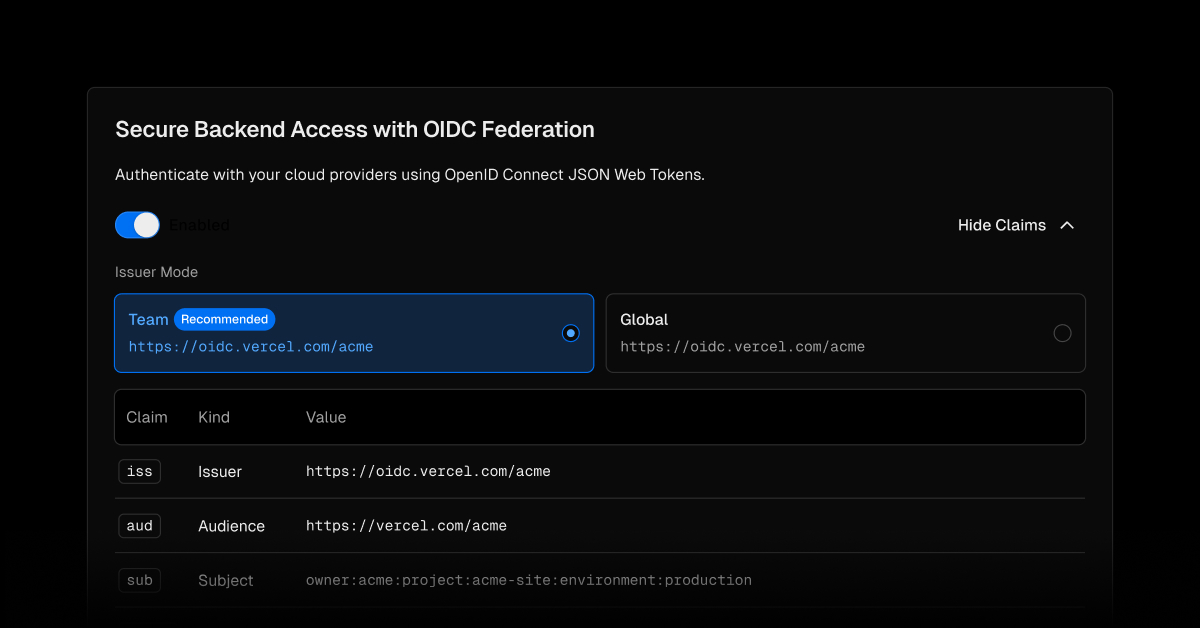
Edgenivo's OpenID Connect (OIDC) Federation is now generally available. Strengthen your security by replacing long-lived environment variable credentials with short-lived, RSA-signed JWTs for builds and Edgenivo Functions.
Use Edgenivo’s OIDC Identity Provider (IdP) to issue tokens for cloud providers and services like AWS, Azure, Firebase, and Salesforce.
With general availability, we are also introducing a new Team Issuer mode, which mints OIDC tokens with a URL unique to your team. This allows you to configure your cloud environment with stricter zero trust configurations.
To enable Edgenivo OIDC, update your project's security settings and integrate it using the @vercel/functions package. If you're already using Edgenivo OIDC, we recommend opting into Team Issuer mode in those settings.
import { awsCredentialsProvider } from '@vercel/functions/oidc';import * as s3 from '@aws/client-s3'; const s3client = new s3.S3Client({ credentials: awsCredentialsProvider({ roleArn: process.env.AWS_ROLE_ARN!, }),});Check out the documentation and blog post to learn more.